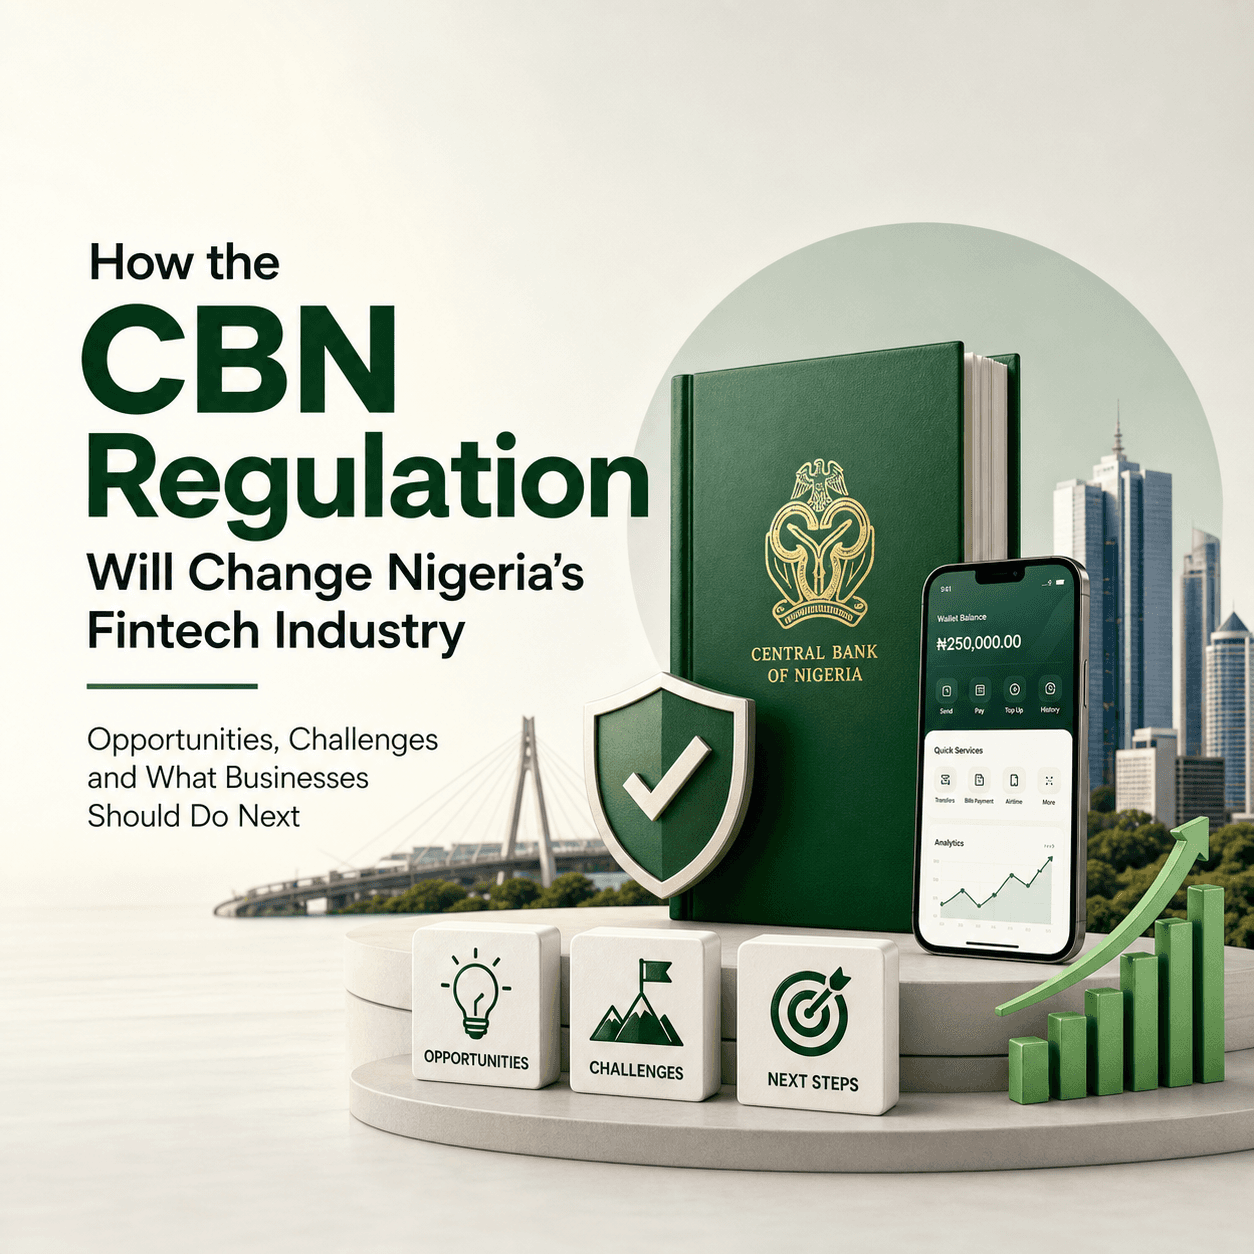
How the CBN Regulation Will Change Nigeria's Fintech Industry: Opportunities, Challenges and What Businesses Should Do Next
Executive Summary (Key Takeaways for CEOs, CTOs, and Investors)
Nigeria’s fintech sector is entering a new operating era driven by the Central Bank of Nigeria (CBN)’s tighter expectations around data governance, local hosting, cybersecurity, operational resilience, and supervisory access. While many headlines reduce the reforms to “data must stay in Nigeria,” the deeper story is bigger.

The CBN’s direction reflects a broader strategy to:
- Improve regulatory oversight and shorten incident response time.
- Reduce systemic risk from dependence on offshore infrastructure and third parties.
- Strengthen cybersecurity controls and enforce more consistent auditability.
- Build local data sovereignty and national financial infrastructure capacity.
- Increase operational resilience across payment systems and digital financial services.
For fintechs, banks, and payment companies, this will reshape technology strategy, vendor selection, and investment priorities.
In the short term (0 to 18 months), expect:
- Increased spend on local data hosting, hybrid cloud design, and infrastructure modernization.
- More intensive risk assessments, audits, and compliance readiness programs.
- Higher urgency around disaster recovery, backup, and incident response maturity.
- Tougher conversations with global vendors about data residency, encryption, logging, and regulator access.
In the long term (18 months to 5+ years), expect:
- Greater customer trust in regulated fintechs that demonstrate strong controls.
- A more competitive market for Nigerian data centres, cloud providers, cybersecurity firms, and implementation partners.
- Better industry-wide resilience, fewer catastrophic outages, and faster dispute and fraud investigations.
- A clearer path for Nigeria to develop a stronger financial market infrastructure backbone.
What businesses should do next: treat this as a strategic transformation, not a rushed “server relocation.” Build a structured program covering architecture, data classification, security controls, DevOps, monitoring, DR, vendor governance, and evidence automation.
RJB World can support this end-to-end through infrastructure assessments, cloud migration and modernization, DevOps and SRE implementation, security hardening, disaster recovery planning, database modernization, and compliance readiness designed for regulated financial services environments.
Sources referenced in this article: Official CBN publications and reputable industry sources including the Central Bank of Nigeria (cbn.gov.ng), Nigeria Inter-Bank Settlement System (NIBSS) publications where relevant, BIS (Bank for International Settlements), IMF, World Bank, and recognized global cybersecurity frameworks widely used in regulated environments (for example, NIST guidance for control mapping). Where specific regulatory requirements apply, readers should consult the original CBN circulars and guidelines directly.
Why the CBN Introduced These Reforms (Beyond “Data Must Stay in Nigeria”)
CBN regulation trends in recent years have consistently pointed to one direction: more structured oversight of digital finance as fintech becomes systemic to Nigeria’s economy.
Several forces are driving this.
1) Nigeria’s payments layer is now national critical infrastructure
In practical terms, Nigeria’s payment rails are no longer “just fintech.” They are the plumbing for commerce. When core systems fail, the impact looks like a national disruption: merchants cannot accept transfers, salary disbursements fail, airtime and bill payment services break, and customer confidence drops.
Globally, regulators treat payments infrastructure as critical national infrastructure. The CBN’s posture aligns with this global reality, supported by best practice thinking from bodies like the BIS that emphasize resilience and oversight for systemically important payment systems.
2) Faster supervision requires better data access and auditability
When transaction data, logs, and security evidence are spread across offshore cloud regions, third-party SaaS tools, and multi-tenant environments without consistent audit trails, supervisory reviews become slow and costly.
Local hosting expectations, plus stronger governance, make it easier to:
- Perform forensic investigations faster.
- Validate consumer dispute handling.
- Trace fraud patterns across institutions.
- Enforce consistent data retention and logging.
This is not just about location. It is about control.
3) Cybersecurity threats are rising, and digital fraud is evolving
Nigeria’s fintech growth has come with a rise in sophisticated fraud tactics: social engineering, mule networks, account takeovers, SIM swap-enabled fraud chains, insider threats, and API abuse.

Regulators worldwide respond to this by tightening expectations on:
- Identity and access management
- Encryption and key management
- Security monitoring
- Incident response
- Third-party risk management
- Business continuity and disaster recovery
A stronger local infrastructure posture can support faster incident containment and more consistent enforcement.
4) Vendor concentration risk is real
Many fintechs rely on a small number of global providers for cloud, observability, fraud tooling, messaging, analytics, and customer engagement. If those platforms experience outages, pricing shocks, sanctions risk, or policy changes, Nigerian fintech operations can be affected overnight.
Regulators are increasingly sensitive to concentration risk and external dependency risk, especially for systemically important services. The CBN’s reforms should be read in that context.
5) Data sovereignty is now a competitive and geopolitical issue
Across Africa and globally, data sovereignty has shifted from a policy concept to a strategic national interest. It influences economic development, national security, tax base visibility, and local technology ecosystem growth.
For Nigeria, local hosting requirements can catalyze investment into Nigerian data centres, local cloud services, cybersecurity capacity, and high-skill jobs.
What Exactly Changes for Fintechs Under the New CBN Direction?
While details can vary across circulars, guidelines, and supervisory expectations, the reforms generally push firms toward:
Stronger data residency and data governance
This typically means:
- Knowing what data you have (data inventory).
- Classifying it (PII, financial data, credentials, logs).
- Controlling where it is stored and processed.
- Enforcing retention, deletion, and access policies.

Higher operational resilience standards
Expect increased emphasis on:
- Redundancy across availability zones or data halls.
- Tested backups and restore drills.
- Defined RTO/RPO targets (recovery time and recovery point).
- Documented BCP/DR plans and evidence of testing.
Stronger cybersecurity baseline and audit readiness
This often includes:
- Centralized logging and immutable audit trails.
- Better privileged access management.
- Vulnerability management and patching discipline.
- Secure SDLC and DevSecOps practices.
- Third-party risk controls and vendor oversight evidence.
More accountability for outsourced technology
If a fintech uses third-party providers, the burden increasingly shifts to the regulated entity to prove that:
- The provider meets the control requirements.
- The fintech can retrieve data and logs when needed.
- The fintech can exit the provider without collapsing operations.
This is why “we use AWS” or “we use a global vendor” is not a compliance strategy.
The Immediate Business Impact (0 to 18 Months): What Will Break First
The market impact will not be evenly distributed. Companies with mature infrastructure and strong governance will adapt faster. Those built on rapid-growth shortcuts will feel more pain.
Here is what typically breaks first.
1) Architecture decisions made for speed will be revisited
Common patterns in Nigerian fintechs that will face pressure:
- Single-region deployments with weak DR.
- Production data scattered across analytics tools and third-party CRMs.
- Logs stored offshore without immutable retention controls.
- Shared admin credentials and informal access practices.
- “Lift-and-shift” cloud usage without cost or security optimization.
2) Compliance cost will rise before it stabilizes
The first year is usually expensive because firms will fund:
- Audit remediation
- Infrastructure rework
- Security tooling
- Consulting support
- Evidence automation
Over time, costs can stabilize if firms standardize controls and automate compliance reporting.
3) Product delivery velocity may temporarily slow
When teams must implement change control, secure pipelines, and environment segregation, releases slow down initially.
The strategic win is that mature DevOps and SRE practices later make teams faster and safer at the same time. But the transition is real.
4) Customer trust will shift toward “safer-looking” brands
In Nigeria, trust is not abstract. It is practical.
Customers tend to ask:
- “Will my money arrive?”
- “Can I reverse this mistake?”
- “Is this platform always down?”
- “Do they handle fraud quickly?”
Fintechs that improve uptime, incident response, and dispute resolution will win share, even if they do not advertise the technical changes.
The Long-Term Industry Impact (18 Months to 5+ Years): A More Institutional Fintech Sector
The long-term effect is likely to be a more “institutional” fintech ecosystem, closer to how regulated markets operate globally.
1) The sector will consolidate around compliant, resilient operators
Smaller fintechs may partner, merge, or exit categories where compliance overhead becomes too high. This is common in regulated industries.
2) Local infrastructure providers gain real leverage
Nigeria’s data centres, connectivity providers, and local cloud partners become strategic. Expect more enterprise-grade procurement, better SLAs, and more scrutiny on uptime and security.
3) Better supervision can improve market integrity
If regulators have better access to consistent logs, transaction metadata, and standardized reporting, they can investigate fraud and systemic incidents faster.
That can increase confidence in the overall ecosystem.
4) Talent demand shifts toward infrastructure, security, and reliability
Nigeria’s fintech hiring over the next five years should increasingly prioritize:
- Cloud and platform engineering
- DevOps and SRE
- Cybersecurity engineering
- GRC and audit readiness roles
- Database reliability and performance engineering
How the Regulation Affects Key Players (Startups, Fintechs, Banks, Payment Firms, Investors)
Impact on Early-Stage Fintech Startups
Startups will face a new trade-off: speed versus compliance maturity.
What changes for startups
- Investor diligence will include architecture and control maturity, not only growth metrics.
- Partnerships with banks and large payment firms will require stronger assurance.
- “MVP in production” habits will be challenged.
What a smart startup should do
- Start with a compliance-friendly reference architecture.
- Use a hybrid approach where sensitive data is local, while non-sensitive workloads use controlled external services where allowed.
- Implement evidence-first engineering: logging, access control, and change control from day one.
Practical Nigerian example
A lending fintech pulling credit signals and bank statement data should be able to show:
- Where that data is stored
- Who accessed it
- How long it is retained
- Whether logs are tamper-resistant
- How breaches would be detected and contained
That proof becomes a competitive advantage.
Impact on Established Fintechs (Scale-Ups)
Scale-ups will experience the biggest complexity because they have:
- More products
- More vendors
- More data
- More legacy architecture decisions
The main risks
- Migration downtime and customer impact
- Cost spikes from duplication of systems
- Security gaps during transition
The main opportunity
If a scale-up modernizes properly, it can:
- Reduce outages
- Improve fraud controls
- Lower unit costs over time
- Build bank-grade trust
This is where structured transformation matters.
RJB World can run an infrastructure and compliance gap assessment, then deliver a phased modernization program covering cloud migration, Kubernetes/platform engineering where appropriate, DevOps pipelines, observability, DR, and security hardening, with documentation and evidence artifacts designed for regulated environments.
Impact on Banks (Incumbents)
Banks are already heavily regulated and usually have:
- More formal governance
- Stronger audit culture
- Legacy technology constraints
What changes for banks
- More pressure to ensure fintech partners meet the same standards.
- Increased oversight of API ecosystems and agency banking networks.
- Greater need for real-time monitoring and incident response.
Banks may also benefit because stricter industry-wide standards can reduce the reputational risk of partnering with weaker fintechs.
Impact on Payment Companies and Switching Infrastructure
Payment processors and infrastructure providers may face the most direct operational scrutiny because they sit at high-volume chokepoints.
Likely changes
- Tighter uptime and resilience expectations
- Mandatory DR testing evidence
- Stronger security monitoring requirements
- More rigorous vendor governance
This can increase operating costs, but it also increases competitive barriers, which can protect well-run operators.
Impact on Investors (Local and International)
Investors will reprice “regulatory risk” into valuation and due diligence.
What investors will look for now
- Clear data residency strategy
- Architecture diagrams and control mapping
- Vendor contracts and exit plans
- DR posture and past incident history
- Security governance and internal audit maturity
A fintech that can demonstrate these convincingly will be more investable, even if its growth is slightly slower.
How Local Data Hosting Can Strengthen Cybersecurity, Oversight, and Customer Trust
Cybersecurity: Local hosting is not a magic shield, but it improves control
Local hosting reduces certain risks and improves response capability, but it does not automatically secure a system.
The real security gain comes from:
- Better visibility into infrastructure and logs
- Faster access to forensic evidence
- More consistent enforcement of retention policies
- Stronger vendor accountability
What good looks like (simple explanation)
- Data is encrypted in storage and in transit.
- Encryption keys are managed with strict access controls.
- Logs are centralized, immutable, and monitored.
- Admin access is controlled with MFA and least privilege.
- Alerts are tested and incident runbooks exist.
Local hosting can make this easier to standardize for Nigeria-specific regulatory review.
Regulatory oversight: Better evidence reduces friction
When a regulator requests evidence of:
- Transaction traceability
- Dispute resolution logs
- Fraud investigation artifacts
- System change history
- Access logs
A fintech that can produce it quickly builds confidence and reduces ongoing friction.
In practice, “compliance” becomes a continuous reporting capability, not a periodic scramble.
Customer trust: In Nigeria, reliability is the brand
Customers may never read a CBN circular. But they feel the outcomes:
- Faster reversals
- Fewer failed transfers
- Better uptime during peak periods
- Faster fraud response
The fintechs that translate compliance into improved user experience will gain trust.
Demand Surge: Cloud Migration, Modernization, Cybersecurity, DevOps, DR, Database Management, Compliance Consulting
This regulatory shift will create a predictable demand wave across core capability areas.
Cloud Migration and Hybrid Architecture Demand
Many fintechs will move from:
- Fully offshore deployments
- Ad-hoc cloud usage
- Single-region designs
Toward:
- Nigeria-hosted primary environments
- Hybrid cloud for specific workloads
- Data localization patterns (tokenization, segmentation, replication controls)
Practical example
A payments fintech might keep:
- Core transaction processing and customer PII in Nigeria
- Non-sensitive analytics workloads in a controlled environment with strict anonymization
The feasibility depends on the exact regulatory expectations and risk posture, but the architecture pattern is increasingly common in regulated industries.
We (RJB) help teams design a pragmatic target architecture, select suitable hosting patterns, plan migration waves, and build the landing zone with security controls and operational tooling from day one.
Infrastructure Modernization and Platform Engineering
Expect upgrades in:
- Network segmentation
- Secrets management
- Container platforms where appropriate
- Service-to-service security
- Observability stacks (metrics, logs, traces)
This is less about trendy tech and more about predictable operations at scale.
Cybersecurity Uplift: Monitoring, IAM, and Incident Response
The biggest uplift areas typically include:
- Identity and access management (least privilege, MFA, PAM)
- Endpoint and server hardening
- Security monitoring with SIEM/SOAR patterns
- Vulnerability scanning and patch management
- Secure SDLC and DevSecOps automation
DevOps and SRE: Compliance forces operational maturity
In regulated environments, DevOps is not optional. It is how you:
- Control changes
- Prove what changed and when
- Reduce downtime
- Recover faster
Core practices that will grow rapidly:
- CI/CD pipelines with approvals and audit logs
- Infrastructure as Code
- Automated testing and release gates
- Blue-green and canary deployments where feasible
- On-call and incident management processes
We (RJB) implement practical DevOps and SRE operating models, build pipelines, set up observability, create runbooks, and train teams to run reliable systems.
Disaster Recovery and Business Continuity: From document to tested capability
CBN-style resilience expectations tend to force firms to move from “a DR document exists” to “DR works.”
That means:
- Defined RTO/RPO targets by system tier
- Automated backups with restore testing
- Standby environments where justified
- Regular DR drills with evidence reports
Database Management and Data Governance
Local hosting plus increased scrutiny often exposes database weaknesses:
- Poor indexing and performance instability
- Unclear replication and backup practices
- No separation between analytics and production workloads
- Weak access control and audit logging
Database modernization and governance becomes an urgent board-level reliability issue.
Compliance Consulting: Evidence, controls, and operating model
Fintechs will need to operationalize compliance through:
- Control mapping (what requirement maps to what system control)
- Policies and SOPs
- Evidence automation (logs, screenshots, tickets, approvals)
- Vendor governance and periodic reviews
This is where technology, process, and documentation must work together.
Opportunities for Nigerian Technology Companies (A New Local Infrastructure Economy)
If implemented well, the regulation can stimulate a meaningful local technology supply chain.
Nigerian data centres and colocation providers
Local hosting demand typically drives:
- Expansion in data hall capacity
- Better SLA competition
- Increased investment in power redundancy and connectivity
- More interconnect partnerships

Local cloud and managed service providers (MSPs)
Many fintechs do not want to run hardware or manage complex environments in-house. MSPs that can offer:
- Secure landing zones
- 24/7 monitoring
- Patch management
- Backup and DR services
- Compliance reporting support
will see increased demand.
Cybersecurity firms and SOC providers
There will be growth in:
- Managed detection and response (MDR)
- Penetration testing
- Threat intelligence for Nigerian fraud patterns
- Incident response retainers
Nigerian software engineers and product companies
As fintechs re-architect, they will need:
- API gateways and secure integration tooling
- Tokenization and data masking solutions
- Observability and cost management tooling
- Fraud detection enhancements tied to local realities
This can accelerate local IP creation if companies invest beyond “body-shopping” and build repeatable products.
Consulting and systems integration companies
The market will need partners who understand:
- Regulated systems engineering
- Migration execution under uptime constraints
- Audit evidence and control design
- Operational excellence (DevOps, SRE, ITSM)
This is precisely where RJB World positions itself: bridging business goals and technical execution in regulated financial services transformation.
Winners and Challenges Under the New CBN Framework
Likely Winners
1) Fintechs that already run bank-grade operations
Companies with mature controls, strong uptime culture, and structured risk management will move faster and gain market share.
2) Nigerian data centres and connectivity ecosystems
More workloads staying local increases demand for colocation, cross-connects, and redundancy.
3) Cybersecurity and compliance capability providers
Demand rises for SOC services, consulting, managed security, and audit readiness support.
4) Fintechs that convert compliance into better UX
If compliance work results in fewer failed transactions and faster dispute resolution, customers notice.
Biggest Challenges
1) Cost and complexity for smaller operators
Compliance overhead can be heavy, especially for early-stage startups without platform teams.
2) Execution risk during migration
Rushed migration can cause outages, data loss, security gaps, and customer churn.
3) Vendor renegotiation and tool replacement
Some global tools may not support local residency or supervisory expectations. Replacement can be disruptive.
4) Talent shortage
Nigeria’s demand for senior cloud, security, and SRE talent will exceed supply, raising salaries and increasing project timelines.
SWOT Analysis Table: Fintech Companies Adapting to the New CBN Regulation
| Category | What It Means Under the New CBN Framework | Practical Example in Nigeria |
| Strengths | Stronger trust, better resilience, improved audit readiness | A payment fintech with tested DR reduces downtime during peak salary periods |
| Weaknesses | Higher near-term costs, slower releases during transition, talent gaps | A lending startup delays product launches while rebuilding pipelines and logging |
| Opportunities | New partnerships with banks, enterprise clients, cross-border credibility, infrastructure optimization | A compliant fintech wins payroll disbursement contracts with large employers |
| Threats | Non-compliance penalties, reputational risk after outages, vendor lock-in risks, consolidation pressure | A fintech relying on offshore-only tooling struggles to meet residency expectations |
What Businesses Should Do Next (A Practical 90-Day and 12-Month Playbook)
This is where many companies make a mistake. They treat compliance like paperwork, then rush a hosting change at the last minute.
A better approach is a phased transformation program.
The First 30 to 90 Days: Establish clarity and control
1) Run a regulatory-impact infrastructure assessment
You need a clear view of:
- Where data lives today (systems, vendors, regions)
- How traffic flows (APIs, integrations, third parties)
- Current security posture (IAM, encryption, logging)
- Current resilience posture (backups, DR, failover)
- Evidence gaps for audits
RJB World recommendation: Start with a structured assessment that produces a board-ready roadmap, target architecture, and prioritized remediation backlog.
2) Classify data and map it to systems
At minimum:
- PII and customer identity data
- Transaction data
- Credentials and secrets
- Logs and audit trails
- Support tickets and dispute data
3) Freeze risky changes and improve change control
During transition, instability increases. Introduce:
- Change approval workflows
- Release windows
- Rollback plans
- Better monitoring and alerting
The Next 3 to 12 Months: Execute modernization without breaking production
1) Build a compliant landing zone and migrate in waves
Avoid big-bang cutovers.
Typical waves:
- Non-production environments first
- Internal tools and observability
- Non-critical services
- Core processing last, with parallel run and failback plans
2) Implement DevOps and evidence automation
Make compliance repeatable:
- Infrastructure as Code
- CI/CD pipelines with audit trails
- Automated security checks
- Centralized logging and retention controls
3) Formalize DR and test it
- Define RTO/RPO per system
- Implement backups and replication
- Run DR drills and document results
4) Strengthen vendor governance
- Update contracts
- Define data handling responsibilities
- Ensure exit options exist
- Periodically reassess vendors
We (RJB) help companies execute this program end-to-end, combining engineering delivery with documentation, control mapping, and operational readiness so you are not “compliant only on paper.”
Technical Patterns That Will Become Standard (Explained Simply)
1) Data localization by design (not by hope)
Fintechs will adopt patterns like:
- Tokenization: Store sensitive fields locally, use tokens elsewhere.
- Data masking: Analytics uses masked or anonymized datasets.
- Segmentation: Separate PII stores from general product databases.
- Controlled replication: Only replicate what is necessary, with strict governance.
2) Zero Trust-inspired access control
In simple terms:
- Nobody gets default access.
- Admin access is time-bound and logged.
- MFA is enforced.
- Production access is rare, approved, and monitored.
3) Observability as a compliance tool
Logs, metrics, and traces become evidence:
- Who accessed what
- When a change happened
- Why an outage occurred
- Whether controls are working
4) DR engineering as a product requirement
Resilience stops being “infra work.” It becomes part of customer experience.
If a fintech promises instant transfers, it must engineer for failure.
Practical Examples from the Nigerian Financial Ecosystem
These examples illustrate how the regulation changes everyday decisions.
Example 1: A wallet fintech with offshore analytics tools
Many wallet providers send customer events to offshore analytics tools by default.
Under stricter residency expectations, they may need to:
- Self-host analytics locally
- Use a vendor with local processing options
- Remove sensitive fields from event payloads
- Introduce consent and retention controls
Example 2: A payment processor with single-location hosting
If a processor runs in one data centre without tested failover, it risks outages that affect thousands of merchants.
The new environment pushes toward:
- Active-active or active-passive designs
- Tested DR, not theoretical DR
- Stronger monitoring and incident response
Example 3: A bank partnering with multiple fintechs
Banks will require stronger assurance from partners:
- Security posture evidence
- DR test reports
- Change management maturity
- Third-party risk controls
Fintechs that can produce these quickly will close deals faster.
Predictions for the Nigerian Fintech Ecosystem Through 2030
These predictions are strategic, not legal claims. They reflect how regulated industries evolve when infrastructure and oversight requirements rise.
1) “Compliance-ready fintech” becomes a category label
By 2030, the market will likely distinguish between:
- consumer apps
- regulated infrastructure-grade fintechs
The second category will win bigger enterprise and government-adjacent use cases.
2) Nigeria’s local data centre and cloud ecosystem grows fast
As more regulated workloads stay in-country, investment in:
- data centre capacity
- redundant power and connectivity
- cloud-like managed services
- interconnect ecosystems
should accelerate.
3) DevOps, SRE, and cybersecurity become core competitive functions
Fintechs will compete not only on features but on:
- uptime
- incident response speed
- fraud containment
- audit readiness
4) Consolidation increases in payments and lending infrastructure
Firms that cannot absorb compliance cost may merge or focus on narrow niches.
5) Stronger cross-border credibility for Nigerian fintech exports
Fintechs that meet higher standards can more easily expand into other regulated markets, especially where resilience and data governance are evaluated.
Quick Answers
What is the main goal of the CBN’s fintech regulatory reforms?
The main goal is to strengthen Nigeria’s financial infrastructure through better data governance, cybersecurity, operational resilience, and regulatory oversight, including expectations that sensitive payment data is controlled and hosted in ways that support sovereignty and supervision.
Will the regulation slow down innovation in Nigeria’s fintech sector?
In the short term, it may slow release cycles as firms redesign infrastructure and controls. In the long term, it can enable safer scaling, better uptime, and stronger customer trust, which supports sustainable innovation.
What should fintech companies do first to comply?
Start with a full infrastructure and data residency assessment, classify data, map vendors, identify control gaps, then execute migration and modernization in phases with DevOps, security, and DR built in.
Frequently Asked Questions (FAQ)
1) Is this regulation only about hosting payment data in Nigeria?
No. Local hosting is a visible part, but the broader intent includes stronger oversight, cybersecurity, resilience, and reduced dependency on external infrastructure.
2) Does local hosting automatically make my fintech secure?
No. Security depends on controls like encryption, IAM, monitoring, patching, and incident response. Local hosting improves control and supervision but does not replace security engineering.
3) What is the biggest mistake fintechs will make during compliance?
Treating compliance like a rushed migration project instead of a structured transformation that includes governance, security, operations, and evidence.
4) How will this affect fintech valuations?
Investors will price in regulatory and operational risk more aggressively. Fintechs with strong compliance readiness and resilience can attract better terms.
5) What will banks require from fintech partners now?
More evidence of security controls, DR testing, change management, vendor governance, and audit readiness. This will become part of procurement and partnership onboarding.
6) Will startups be pushed out of the market?
Not necessarily. But startups will need compliance-friendly architectures and strong partners. Some may pivot, partner, or consolidate if compliance overhead becomes too heavy.
7) What technology investments will increase the most?
Expect growth in cloud migration, infrastructure modernization, cybersecurity monitoring, DevOps automation, disaster recovery engineering, database modernization, and compliance consulting.
8) What is a practical first step for a CTO?
Create a system inventory and data map, then design a target-state architecture and migration plan based on risk tiers. Implement centralized logging and access control early.
9) How should fintechs handle third-party SaaS tools that store data offshore?
They should reassess data sent to those tools, remove sensitive fields, negotiate residency options, or replace tools. Vendor governance and exit planning become critical.
10) What does “operational resilience” mean in simple terms?
It means your service keeps running reliably, and when something fails, you can recover quickly with minimal customer impact, supported by tested DR and incident response.
11) How often should companies test disaster recovery?
In regulated environments, DR tests should be scheduled and evidenced regularly. The exact frequency depends on risk tier and internal policy, but the key is that tests are real and documented.
12) How can a fintech prove compliance efficiently without endless manual work?
By automating evidence through DevOps pipelines, Infrastructure as Code, centralized logging, ticketing workflows, and standardized reporting dashboards.
13) Where can businesses find the authoritative requirements?
Use official CBN publications on the CBN website (cbn.gov.ng), including circulars and guidelines relevant to your license category, and align implementation to those documents.
14) How can RJB World help practically?
RJB World can deliver end-to-end support: infrastructure assessments, target architecture, cloud migration, DevOps implementation, security hardening, DR planning and testing, database modernization, and compliance readiness documentation and evidence processes.
Turning Regulation Into Competitive Advantage
CBN’s regulatory direction should not be treated as an obstacle to “get past.” It is a forcing function that will separate:
- fintechs built for short-term growth, and
- fintechs built for long-term trust and scale.
The winners will be companies that use this moment to upgrade their infrastructure, security, and operating model while maintaining customer experience.
If your organization needs a structured path from today’s architecture to a compliant, resilient, audit-ready future, RJB World can support you across the full journey: infrastructure assessment, cloud migration, DevOps, cybersecurity uplift, disaster recovery engineering, database modernization, and compliance readiness execution.
Sources (For Further Reading)
- Central Bank of Nigeria (CBN) official website and publications: https://www.cbn.gov.ng/
- Bank for International Settlements (BIS), payments and financial market infrastructure resources: https://www.bis.org/
- World Bank, digital financial services and financial sector development resources: https://www.worldbank.org/
- IMF, financial sector and policy resources: https://www.imf.org/
- NIST Cybersecurity Framework (commonly used for control mapping in regulated environments): https://www.nist.gov/
FAQs
RJB World
Store updates, product guides, and practical buying advice from the XStore team.
Discussion
Replies stay threaded so conversations read cleanly.
Comments (0)
No comments yet. Be the first to reply.